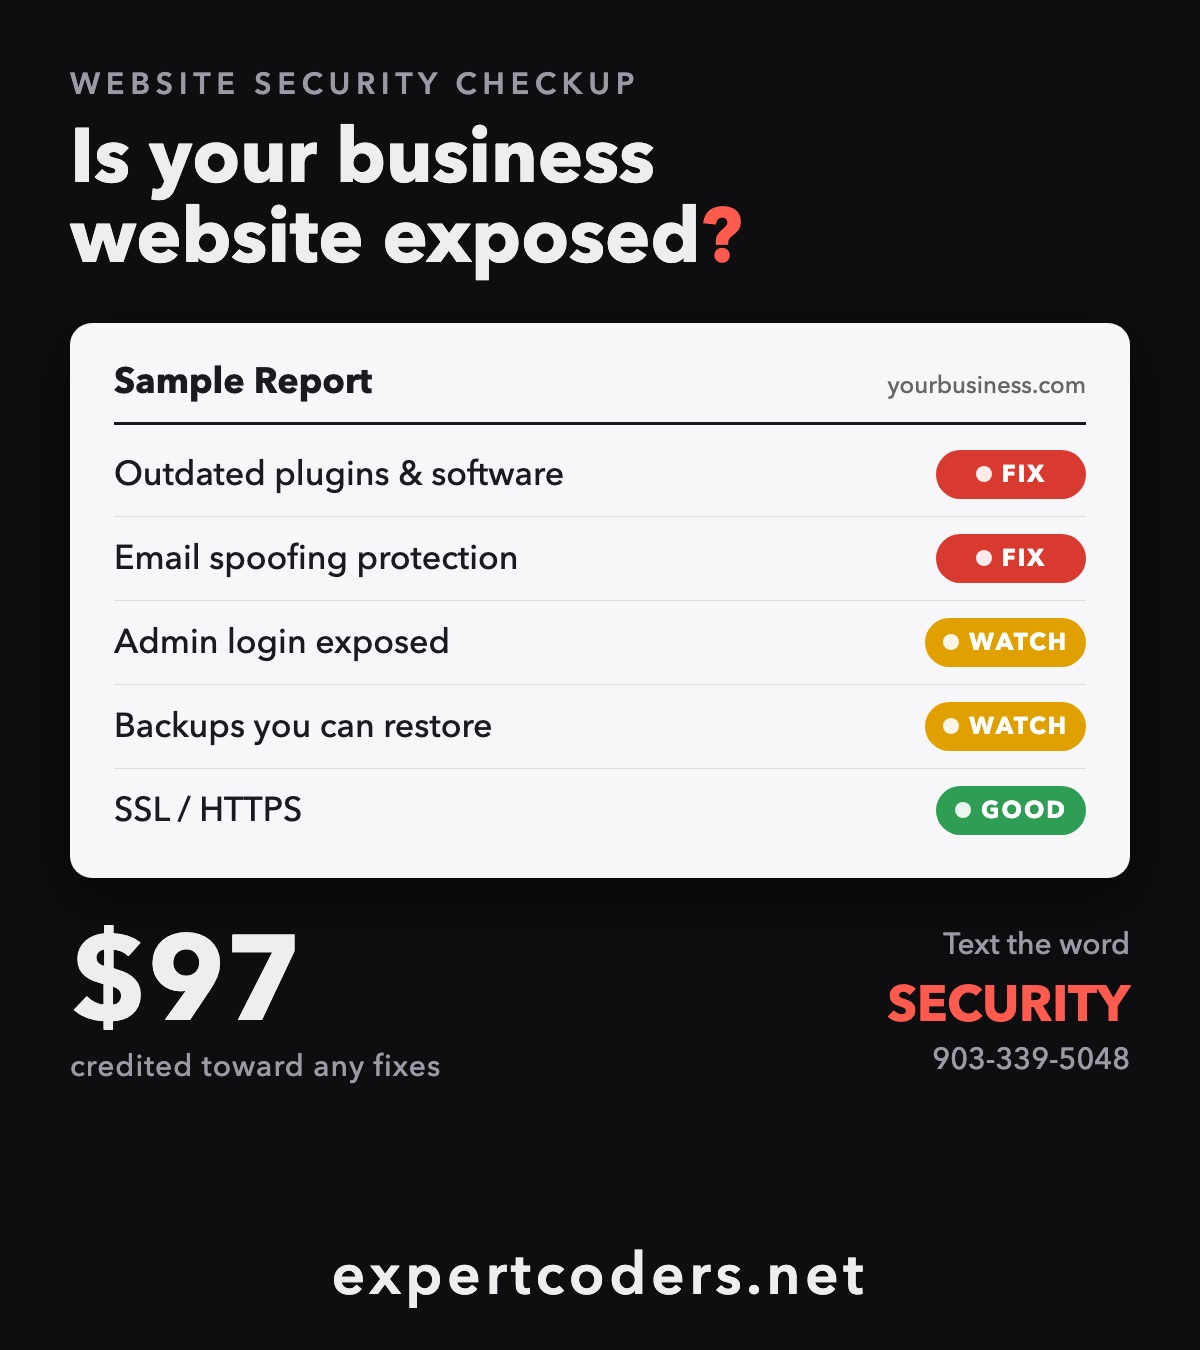
What I check
The open doors most small-business sites have.
Outdated software
WordPress, plugins, themes, and server software with known, published exploits. This is how most small sites get hacked.
Email spoofing
Whether someone can send email that looks like it came from your domain and invoice your customers as you (SPF, DKIM, and DMARC).
Exposed logins and files
Admin pages open to the whole internet, leftover backup files, and pages that should never have been public.
SSL and security headers
Whether your HTTPS setup is solid and your site sends the basic protections browsers expect.
Known data breaches
Whether your domain's email addresses show up in published breach data.
Backups
Whether you actually have a recent backup you could restore if the worst happened.
How it works
Three steps, about a week start to finish.
1. Fill out the form below
Two minutes. It tells me which site to check and gives me your written permission to check it. I never test a site without the owner's permission.
2. I text you a payment link
I review your details first, usually the same business day. If your site is a good fit, I text you a $97 payment link. If it isn't, I'll tell you, and you pay nothing.
3. You get your report and a call
A one-page red, yellow, and green report, plus a 10-minute call to walk you through it. Fix things yourself, hand the report to your current web person, or have me do it.
Non-intrusive, always
No password guessing, no attempts to break in, no load testing. Your site stays up and your visitors never notice a thing.
Request your checkup